Services we provide
Modern Cybersecurity Starts with Visibility
Modern cybersecurity is no longer about tools—it’s about data, visibility, and detection engineering.
Security teams struggle with:
- SIEM complexity
- Data ingestion and pipeline issues
- Lack of deep network visibility
- Inefficient detection workflows
Our Professional Services are built to solve these challenges by combining:
- Next-generation SIEM
- Advanced data pipelines
- Network detection technologies
- Threat intelligence and assessment
👉 We act as your technical partner, not just a service provider.
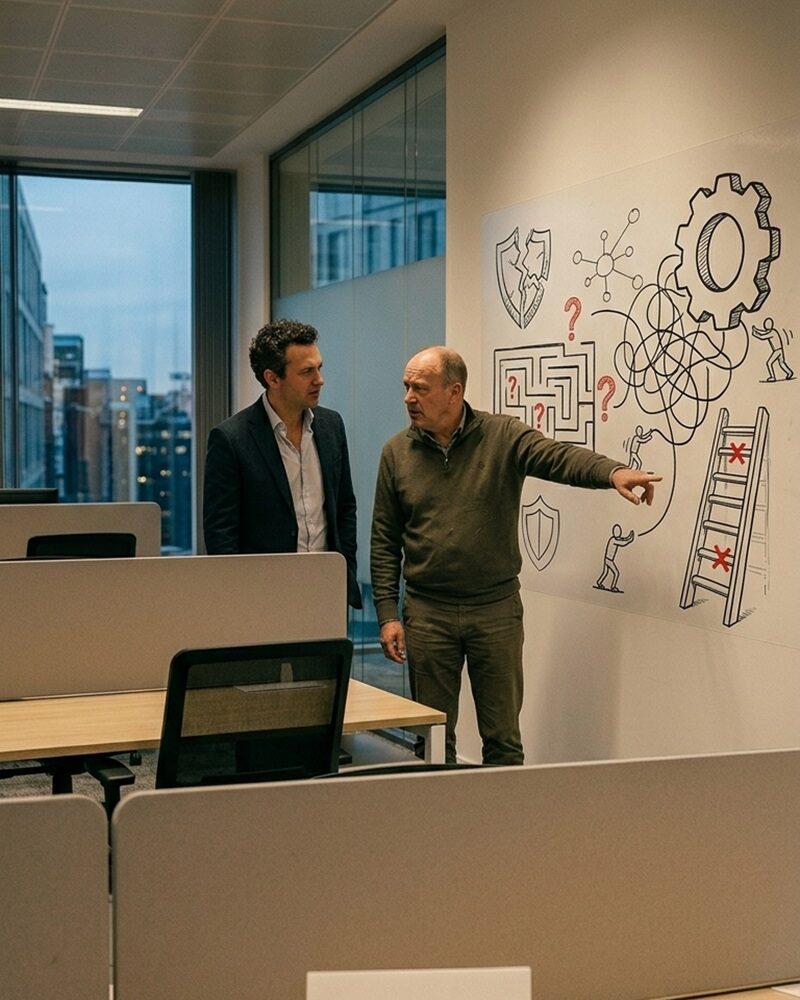
Why Security Operations Break Down
Security operations often break down when organizations lack data visibility, proper log management, effective detections, and the resources needed to manage growing threats.
SIEM platforms overloaded with unstructured data
Poor log ingestion and pipeline inefficiencies
Limited network visibility beyond endpoints
Slow investigation and response times
High false positives and alert fatigue
Lack of actionable threat intelligence
👉 These gaps reduce SOC effectiveness and increase risk.
Engineering-Driven Security for Visibility, Detection & Response
We combine data engineering, detection expertise, and security operations to improve visibility, strengthen threat detection, and accelerate incident response.
Optimized SIEM architecture and integration
High-performance data pipelines
Deep network visibility with NDR
AI-driven detection and faster investigations
Threat intelligence and proactive assessments
Our Professional Services
Our professional services help organizations improve security visibility, streamline operations, strengthen detections, and maximize the value of their SIEM and security investments.
LogScale & Next-Gen SIEM
Build a modern SIEM environment with high-speed ingestion, real-time analytics, and scalable architecture.
What We Do
- SIEM deployment and configuration
- Log onboarding and normalization
- Detection rule development
- Query optimization and performance tuning
- Integration with EDR, NDR, and cloud sources
Why It Matters
Next-gen SIEM integrates multiple data sources to detect threats faster and reduce blind spots
Data Pipeline (Cribl)
Efficiently collect, process, and route security data across your environment.
What We Do
- Log collection and routing
- Data transformation and filtering
- Pipeline optimization
- Cost and storage optimization
- Integration with SIEM platforms
Why It Matters
Clean, structured data improves detection accuracy and reduces noise.
Network Detection (Corelight)
Gain deep visibility into network activity using advanced NDR capabilities.
What We Do
- Deploy network sensors
- Capture full network telemetry
- Detect lateral movement and anomalies
- Integrate network data with SIEM
- Support threat hunting and investigations
Why It Matters
Network-level visibility reveals threats that endpoint tools miss
AI-Driven Detection & Automation
Accelerate threat detection and response using AI-powered analytics.
What We Do
- AI-based anomaly detection
- Automated alert triage
- Faster investigation workflows
- Detection of unknown threats
Why It Matters
AI enables faster detection of evolving threats and reduces manual effort
ThreatAssess (Threat Assessment & Intelligence)
Identify risks, prioritize threats, and strengthen your security posture.
What We Do
- Security posture assessment
- Threat exposure analysis
- Risk prioritization
- Threat intelligence integration
Why It Matters
High-quality threat intelligence reduces false positives and improves response efficiency
Our Engineering-Driven Approach
Our engineering-driven approach focuses on data quality, detection effectiveness, and operational efficiency to deliver stronger visibility, faster response, and measurable security outcomes.
Assessment & Discovery
Architecture & Design
Implementation & Integration
Detection & Optimization
Continuous Improvement
Real Security Challenges We Solve
We help organizations overcome common security challenges, including limited visibility, ineffective detections, data overload, alert fatigue, and resource constraints.
SIEM migration and optimization
Log ingestion and parsing issues
Network blind spots and hidden threats
High alert volume and false positives
Slow incident investigation
Lack of actionable threat intelligence
Why Choose CrowdStrike SOC
CrowdStrike SOC delivers advanced visibility, faster threat detection, streamlined investigations, and scalable security operations to help organizations stay ahead of evolving cyber threats.
Deep expertise in SIEM and detection engineering
Strong experience with LogScale and modern SIEM platforms
Advanced knowledge of data pipelines and integrations
Network detection and threat hunting capabilities
AI-driven detection and automation
Flexible engagement models for resellers and MSSPs
Who We Serve
We support enterprises, MSSPs, security teams, and technology partners seeking stronger visibility, better detections, and scalable security operations.
We partner with:
CrowdStrike Resellers
MSSPs
Enterprise SOC Teams
Security Consultants
Cloud and Hybrid Organizations
Trusted Support Helpful Answers
Find answers to common questions about our services, engagement models, implementation process, security expertise, and ongoing support.