& SIEM Partner
for CrowdStrike
Resellers
Struggling with SIEM, Parsing, or Detection Engineering in CrowdStrike?
and query support so you can deliver faster without building a technical team.
Faster LogScale onboarding
Custom parsing & normalization
Ready-to-deploy detection use cases
Expert query support
Deliver SIEM & SOC Capabilities Without Hiring an In-House Team
We act as your extended technical arm, helping you implement, manage, and optimize CrowdStrike Falcon and Falcon LogScale for faster delivery and better results.
Reduce deployment time
Improve detection accuracy
Scale without increasing cost
Focus on growing your business
Trusted by Security Teams,
MSSPs & Resellers
CrowdStrike-focused expertise
SIEM & detection engineering specialists
Fast onboarding & deployment
Challenges CrowdStrike Resellers Face
Delivering cybersecurity services is not just about tools. It’s about having the right technical backend.
Pain Points
SIEM integration takes longer than expected
Log parsing and normalization become complex
Difficulty building meaningful use cases
Query development and troubleshooting slow down delivery
Note : These challenges impact delivery timelines and client satisfaction
We Handle the
Technical Backend
So You Can Focus on Growth
We work as your technical partner, helping you deliver complete SIEM and SOC capabilities using CrowdStrike Falcon ecosystem.
SIEM Integration
Log Optimization
Threat Detection
Query Support
Our Core Service Areas
Our core service areas are designed to strengthen your SIEM and SOC operations with seamless integrations, expert detection engineering, optimized log management, and reliable support across the CrowdStrike Falcon ecosystem.
Managed Detection & SOC
Managed Detection & SOC
Endpoint & Identity Security
Endpoint & Identity Security
Network, Cloud & Infrastructure
Network, Cloud & Infrastructure
SIEM & Data Engineering
SIEM & Data Engineering
Threat Hunting & Incident Response
Threat Hunting & Incident Response
Security Automation & Integration
Security Automation & Integration
Built for the CrowdStrike Ecosystem
We specialize in the CrowdStrike platform, enabling resellers to deliver advanced security services without technical bottlenecks.
Deep expertise in Falcon platform
Advanced implementation of Falcon LogScale
Faster SIEM onboarding and integrations
Ready-to-deploy detection use cases
Multi-source data integration support
Simple, Structured, and Efficient Process
Our process is designed to keep security operations simple, efficient, and transparent — from onboarding and data normalization to detection engineering and ongoing support, ensuring faster delivery and better operational visibility.
Requirement Discussion
Environment Assessment
Implementation & Setup
Ongoing Support
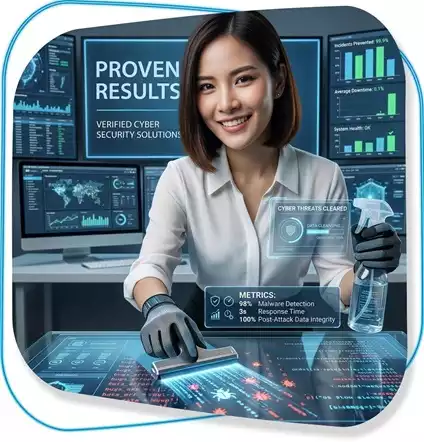
Real Detection Use Cases We Deliver
We develop practical detection use cases focused on real-world threats, helping security teams identify suspicious activities faster, improve response efficiency, and strengthen overall visibility across endpoints, identities, cloud, and network environments.
Cases Result Deliverd
Designed for Security Partners
We work with organizations that deliver security services to their own clients, helping them strengthen SIEM operations, improve detection capabilities, streamline log management, and provide reliable security monitoring and response support at scale.
CrowdStrike Resellers
Managed Security Service Providers
Security Consultants
Why Choose Us as Your Technical Partner